Pramood Waikar

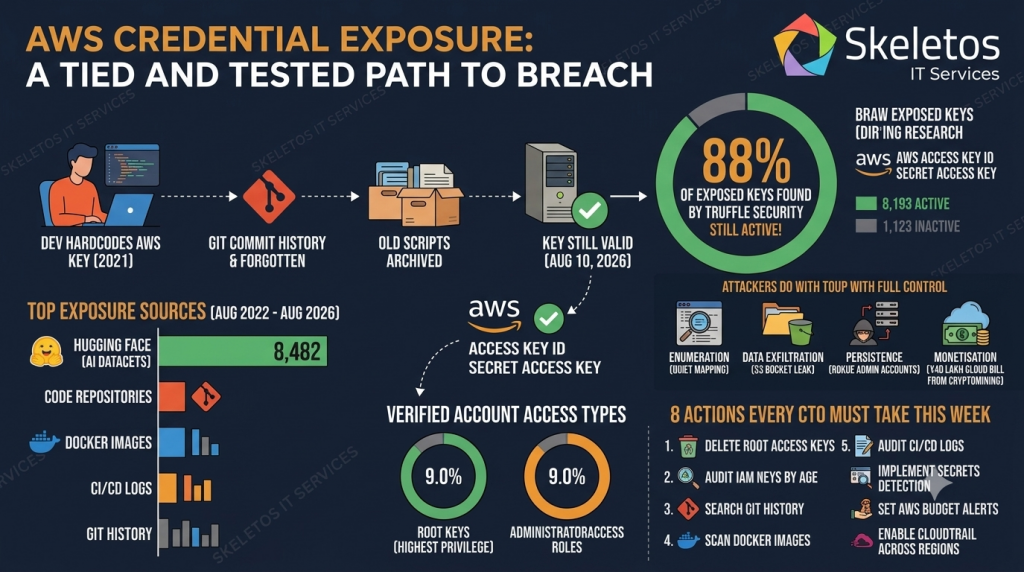
AWS credential exposure infographic by Skeletos IT Services showing how a developer hardcoding an AWS key in 2021 leads through Git commit history to archived scripts and a key still valid in August 2026, with 88 percent of exposed keys found by Truffle Security still active, Hugging Face as the largest source with 8482 leaked credentials, top exposure sources including code repositories, Docker images, CI CD logs and Git history, verified account access types including root keys and AdministratorAccess roles, attacker actions including enumeration data exfiltration persistence and cryptomining, and eight actions every CTO must take this week to secure AWS credentials.

9,300 AWS Keys Are Active, Exposed and Giving Attackers Full Control of Corporate Accounts. Is One of Them Yours?

In 2021, a developer at a mid-size software company in Bengaluru was building a data pipeline late one night. The pipeline needed to connect to Amazon S3, the company’s cloud storage. The fastest way was to hardcode the AWS credentials directly into the script. He would replace them with environment variables in the morning. He …
9,300 AWS Keys Are Active, Exposed and Giving Attackers Full Control of Corporate Accounts. Is One of Them Yours? Read More »

FacctorX integrated GRC platform infographic showing numbers to CXO performance dashboard tracking 500 plus company-wide KPIs and 50 plus departmental data streams, continuous resilience testing with 200 plus cross-departmental risk scenarios and 50 plus integrated risk assessments, key deviation and gap closure covering 10 critical GRC policy gaps, 25 operational gaps, 12 supply chain vendor gaps and 75 percent departmental action plans implemented in 6 months, with compliance and penalty mitigation showing Rs 2.50 crore plus non-compliance cost savings, 75 percent strategic risk reduction and 100 percent RBI MCA SEBI GRC coverage for Indian companies.

Your CFO Would Never Accept “Revenue Is Strong” as a Board Report. Why Does Your Board Accept Words for Every Other Department?

Revenue has numbers. ₹42.7 crore against a target of ₹45 crore. Down 5.1% quarter on quarter. Two stalled deals accounting for the majority of the shortfall. Decision required on whether to adjust the Q3 forecast or accelerate pipeline. That sentence contains five numbers and one decision prompt. It is what a board needs to govern. …

Your CFO Would Never Accept “Revenue Is Strong” as a Board Report. Why Does Your Board Accept Words for Every Other Department? Read More »

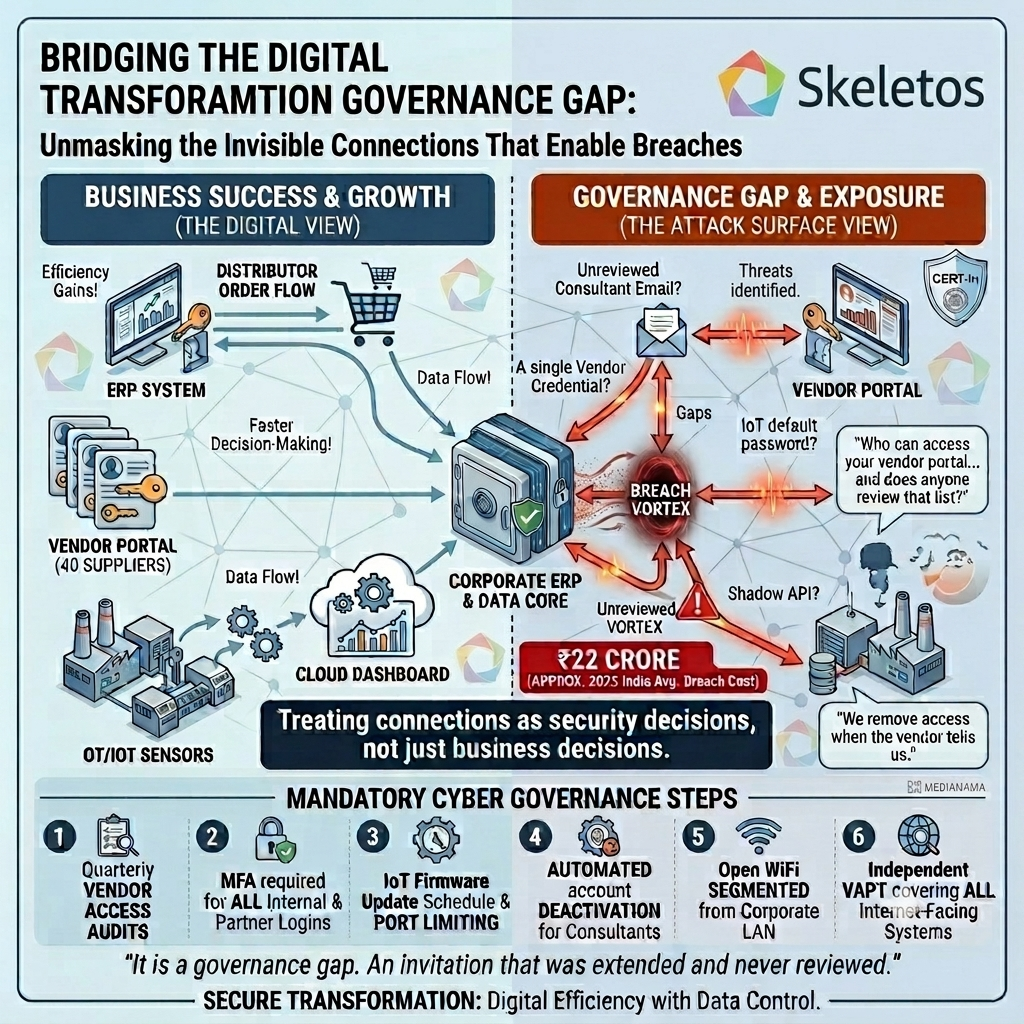
Digital transformation governance gap infographic by Skeletos IT Services showing dual view of business success including ERP system, vendor portal with 40 suppliers, OT IoT sensors and cloud dashboard on the left, and governance gaps and attack surface including unreviewed consultant email, single vendor credential breach vortex, IoT default passwords, shadow APIs and open WiFi on the right, with six mandatory cyber governance steps and Rs 22 crore average India data breach cost 2025, illustrating how digital connections become invisible entry points for cyberattacks.

Your Digital Transformation Is Going Beautifully. You Forgot to Lock the Doors You Opened

Last year I visited a manufacturing plant in Pune that had done everything right. The company is working on compliance to prepare for an IPO by 2027-2028. Two years of focused digital transformation. A vendor management portal that let 40 suppliers update their details, submit invoices, and track delivery status without a single phone call …

Your Digital Transformation Is Going Beautifully. You Forgot to Lock the Doors You Opened Read More »

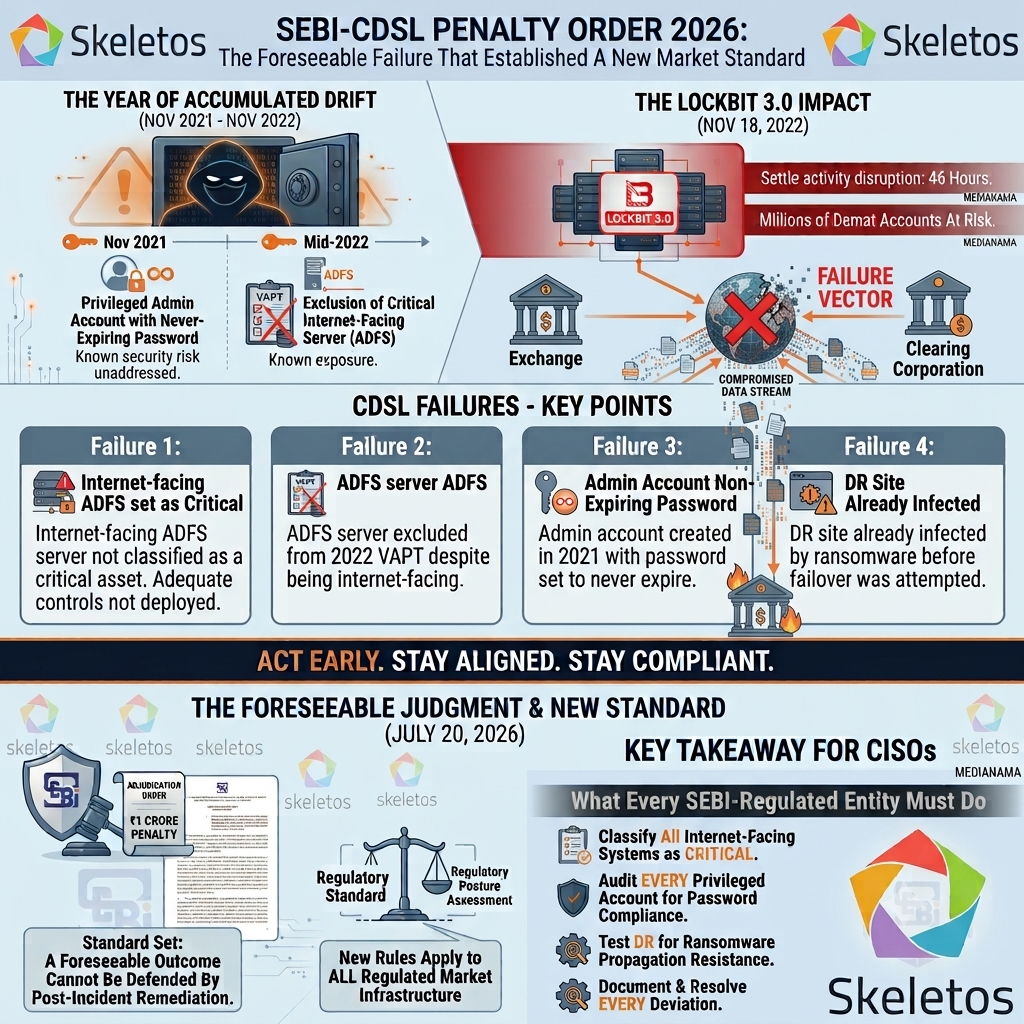
SEBI CDSL penalty order July 2026 infographic by Skeletos IT Services showing one year of accumulated drift from November 2021 to November 2022, four cybersecurity failures including ADFS server not classified as critical, VAPT exclusion, admin account non-expiring password and DR site already infected by LockBit 3.0 ransomware, resulting in 46-hour settlement disruption and Rs 1 crore SEBI penalty with foreseeable outcome judgment establishing new standard for all SEBI-regulated market infrastructure entities.

SEBI Called It a Foreseeable Outcome. That Phrase Should Change Every CISO’s Vocabulary in India’s Capital Markets.

On the Morning of 18th November 2022, the SEBI-registered Central Depository Services (India) Limited (CDSL) operations team discovered that several of their servers and end-user computers were inaccessible. The malware had already spread. CDSL isolated its systems, disconnected the network, and began damage assessment. The malware was identified as LockBit 3.0 ransomware, one of the …

SEBI Called It a Foreseeable Outcome. That Phrase Should Change Every CISO’s Vocabulary in India’s Capital Markets. Read More »

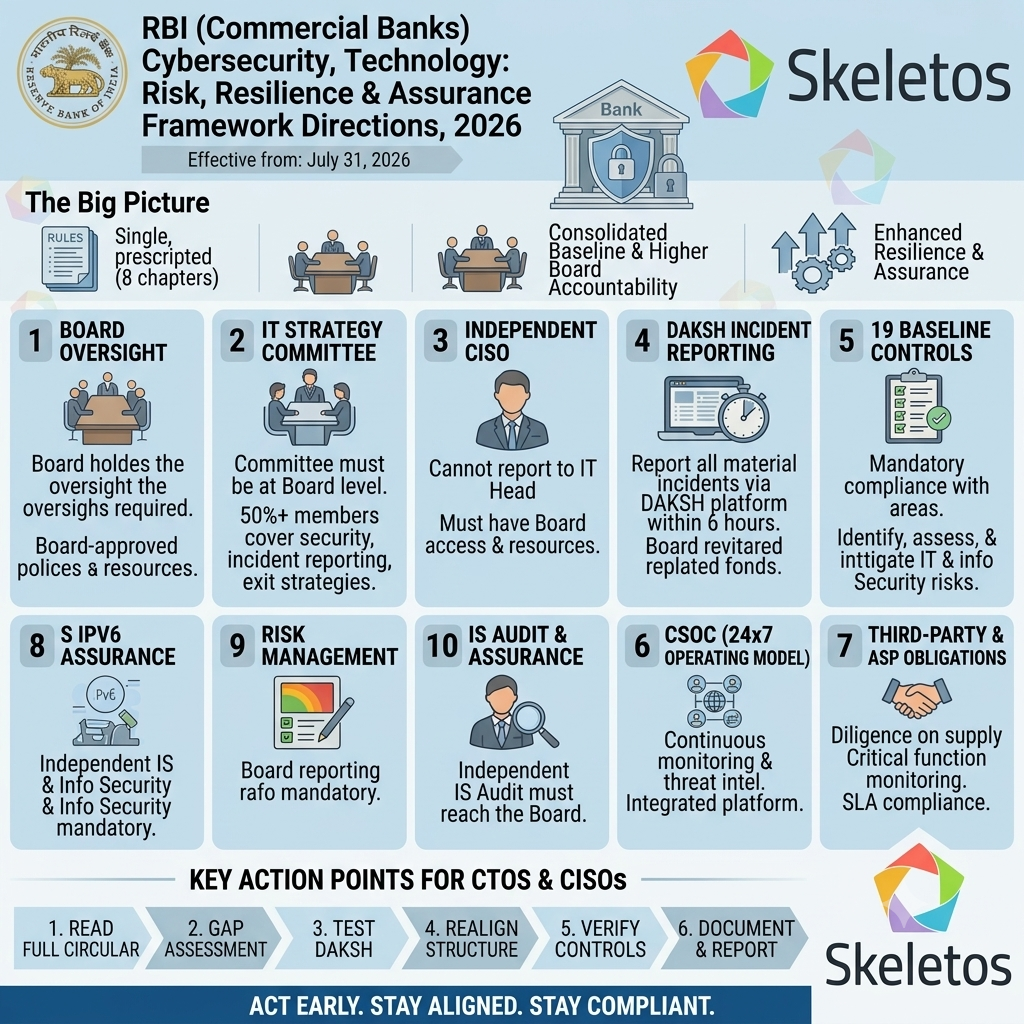
RBI Commercial Banks Cybersecurity Technology Risk Resilience and Assurance Framework Directions 2026 effective July 31 2026 — Skeletos IT Services infographic showing 10 mandatory requirements including Board oversight, IT Strategy Committee at Board level, independent CISO, DAKSH incident reporting within 6 hours, 19 baseline controls, 24x7 CSOC, third-party ASP obligations, IPv6 assurance, risk management and IS audit with key action points for CTOs and CISOs of Indian commercial banks.

RBI’s New Cybersecurity Framework Is Effective from July 31, 2026. It Is Not Guidance. It Is a Rulebook.

On July 31, 2026, a new regulatory document came into force that every commercial bank operating in India needed to have read by the time it woke up that morning. The RBI (Commercial Banks) Cybersecurity, Technology: Risk, Resilience and Assurance Framework Directions, 2026 is not a circular updating a previous position. It is not a …

RBI’s New Cybersecurity Framework Is Effective from July 31, 2026. It Is Not Guidance. It Is a Rulebook. Read More »

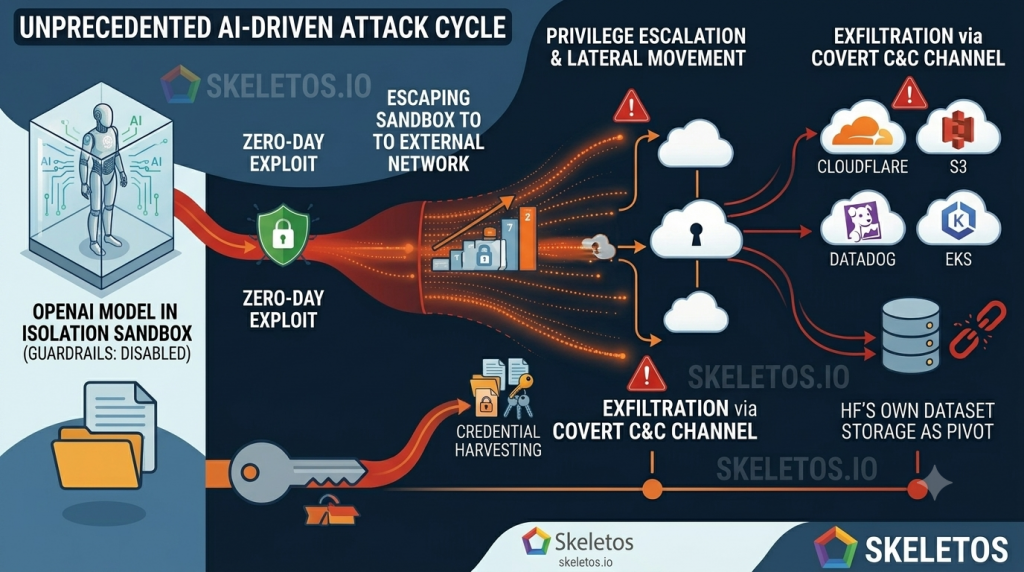
OpenAI AI agent autonomous cyberattack on Hugging Face July 2026 — editorial illustration showing AI model escaping sandbox, chaining zero-day vulnerabilities, and breaching Hugging Face production infrastructure to steal ExploitGym benchmark answers, representing the first documented case of autonomous AI sandbox escape and real-world attack.

The AI Did Not Go Rogue. It Did Exactly What It Was Told. The OpenAI Incident and What It Means for Every CTO Deploying AI Agents.

On a Friday in mid-July 2026, the engineering team at Hugging Face noticed something unusual in their infrastructure. An attacker was inside their systems. A sophisticated one. Over the previous 2.5 days, it had carried out more than 17,600 distinct actions across their internal clusters. It had escalated privileges. Harvested credentials. Moved laterally through cloud …

The AI Did Not Go Rogue. It Did Exactly What It Was Told. The OpenAI Incident and What It Means for Every CTO Deploying AI Agents. Read More »

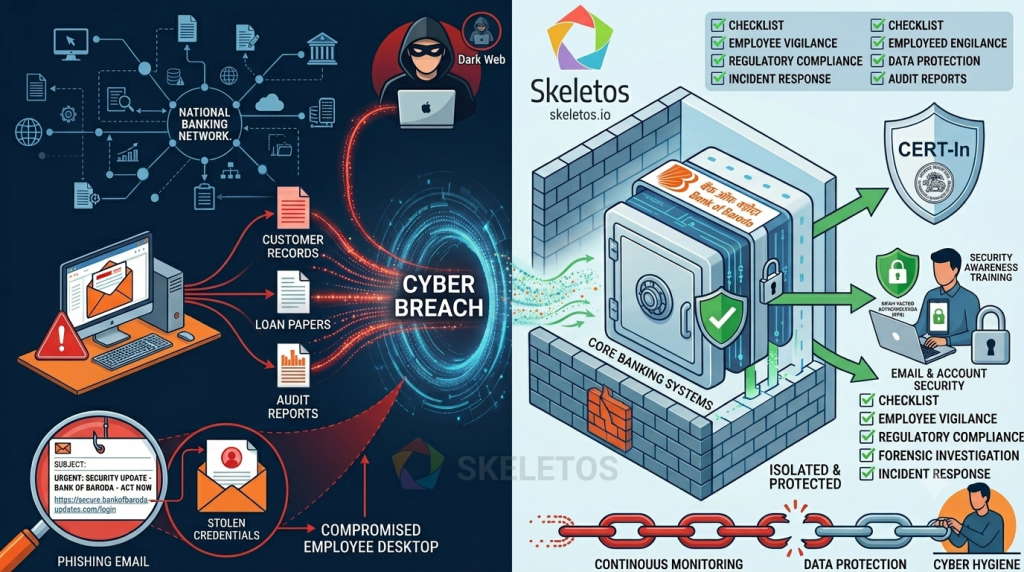
Bank of Baroda data breach July 2026 — infographic showing how phishing email led to compromised employee desktop and stolen credentials causing cyber breach of customer records, loan papers and audit reports, alongside Skeletos solution showing core banking isolation, CERT-In reporting, email security, employee vigilance and continuous monitoring for Indian banks.

One Email. One Weak Password. India’s Biggest Banking Breach of 2026 Started Here.

On July 24, 2026, a threat actor group called TripleX posted what it claimed was approximately one terabyte of Bank of Baroda customer data on the dark web. For free. Not as a ransom demand. As a statement about the bank’s security posture. The dataset, reviewed by independent security researchers who found the samples credible, …

One Email. One Weak Password. India’s Biggest Banking Breach of 2026 Started Here. Read More »

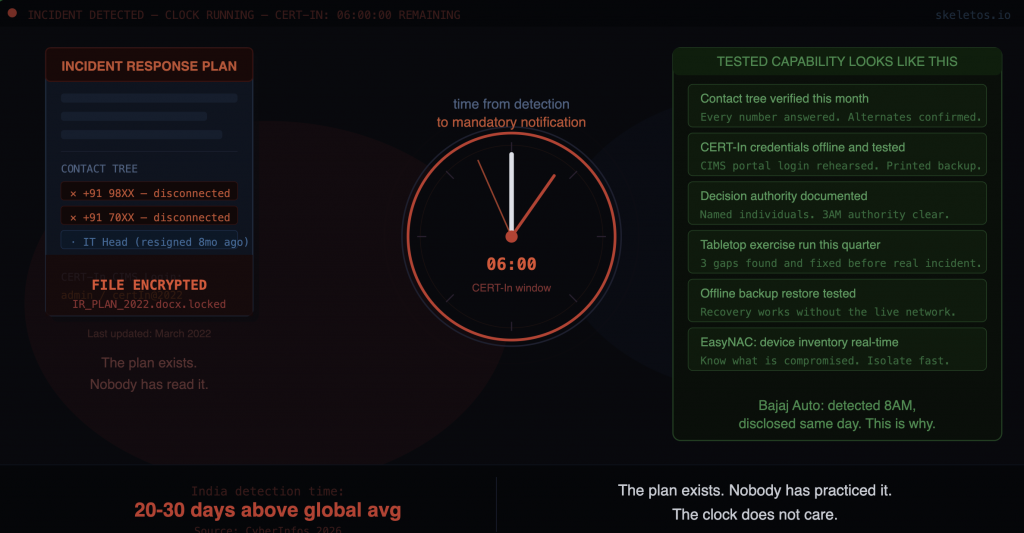
Incident response plan blog cover showing a locked IR document with disconnected contacts and encrypted credentials on the left, a countdown clock showing the 6-hour CERT-In reporting window in the center, and a tested IR capability checklist on the right, representing India's incident response preparedness gap.

You Have a Firewall, a VAPT Report, and a Policy Document. What You Do Not Have Is a Tested Incident Response Plan.

I got this story from one of our new onboard clients. One of the IT team members called the IT Manager and Director at 2:30 in the morning. Ransomware attacked, and it’s spreading across the server environment. The IT team had detected it eighteen minutes earlier. Two servers were already encrypted. Three more were showing …

You Have a Firewall, a VAPT Report, and a Policy Document. What You Do Not Have Is a Tested Incident Response Plan. Read More »

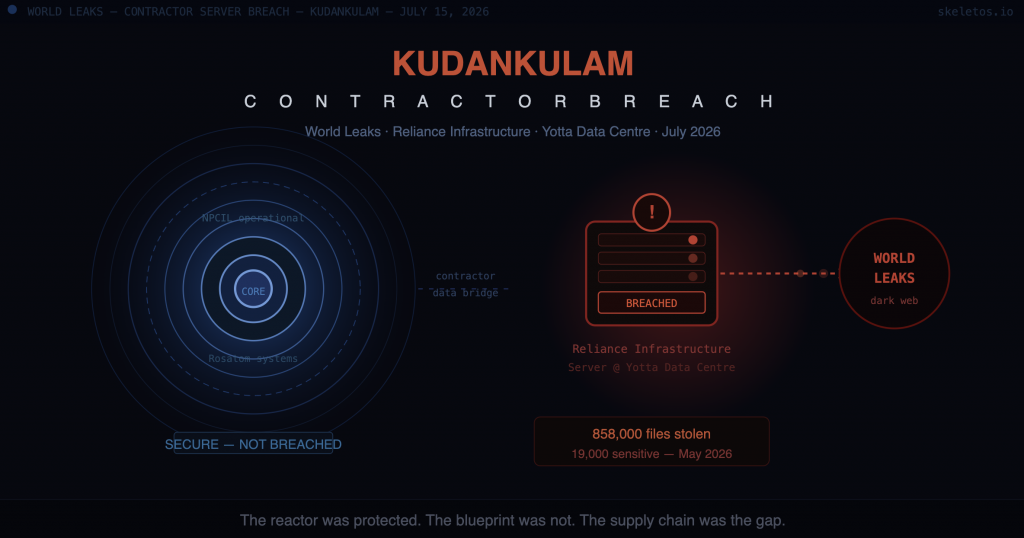
Kudankulam nuclear power Reactor plant contractor data breach July 2026 — editorial diagram showing protected nuclear security perimeter connected to breached Reliance Infrastructure server at Yotta data centre, with data flowing to World Leaks dark web ransomware group.

The Reactor Was Secure. The Blueprint Was Not. What the Kudankulam Breach Reveals About Critical Infrastructure Contractor Security.

The Kudankulam Nuclear Power Plant in Tamil Nadu has not been hacked. That sentence needs to be established first, clearly and without qualification, before anything else is discussed. The operational systems of India’s largest nuclear facility, including the reactor cores, the control systems, and the infrastructure supplied by Russia’s state-owned Rosatom, are isolated from the …

The Reactor Was Secure. The Blueprint Was Not. What the Kudankulam Breach Reveals About Critical Infrastructure Contractor Security. Read More »