Pramood Waikar

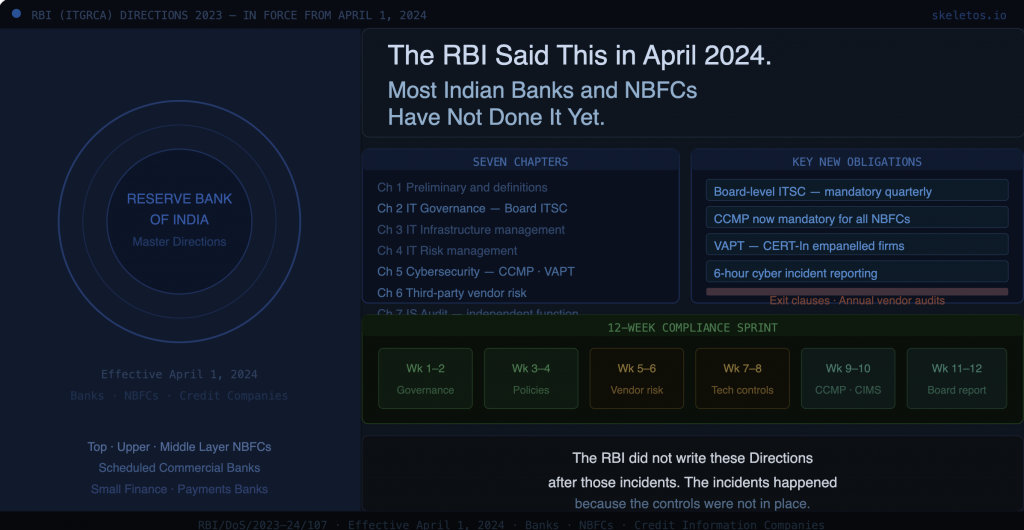
RBI IT Governance Master Directions 2024 compliance guide blog cover showing seven chapter structure, ITSC CCMP VAPT obligations, and 12-week compliance sprint for Indian banks and NBFCs.

The RBI Said This in April 2024. Most Indian Banks and NBFCs Have Not Done It Yet

A few months ago, I was sitting across from the IT head of a mid-size NBFC in Mumbai. A decent-sized company. Upper-middle layer under RBI’s Scale-Based Regulation. A team that takes its work seriously. We were reviewing their security posture when I asked a straightforward question: “Have you constituted your Board-level IT Strategy Committee?” He …

The RBI Said This in April 2024. Most Indian Banks and NBFCs Have Not Done It Yet Read More »
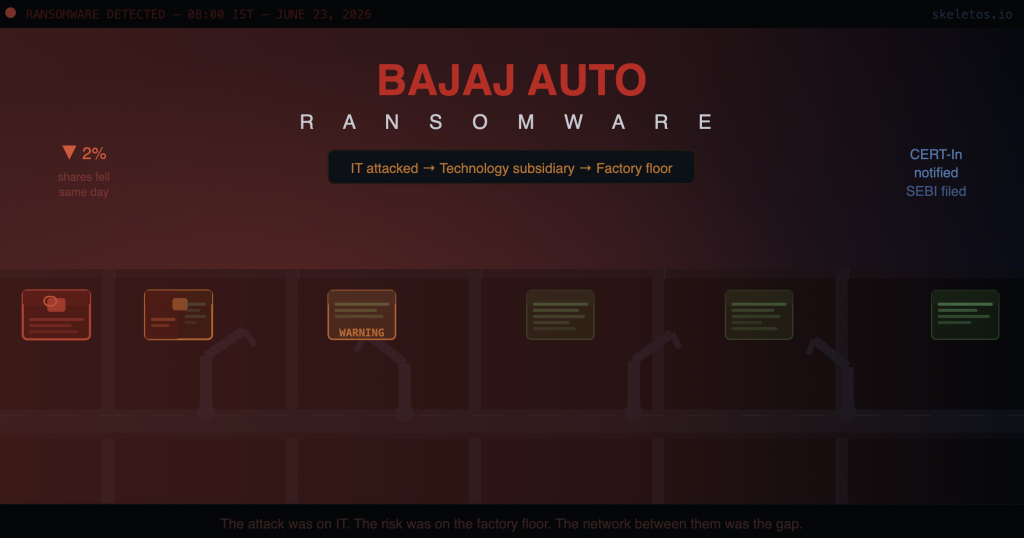
Bajaj Auto ransomware attack June 23 2026 editorial cover showing factory floor screens turning red as ransomware spreads from IT systems through BATL technology subsidiary toward production operations, representing the IT/OT security gap in Indian manufacturing.

The Attack Was on IT. The Risk Was on the Factory Floor. What the Bajaj Auto Ransomware Reveals About India’s Manufacturing Cyber Gap.

Tuesday, June 23, 2026. 8:00 AM IST. A new shift was beginning at one of India’s largest vehicle manufacturers. Workers arriving. Systems booting up. The familiar rhythm of a production day starting. That is when Bajaj Auto’s security team detected it. Ransomware, already active, spreading through the company’s IT infrastructure. Not at 3 AM. Not …

The Attack Was on IT. The Risk Was on the Factory Floor. What the Bajaj Auto Ransomware Reveals About India’s Manufacturing Cyber Gap. Read More »

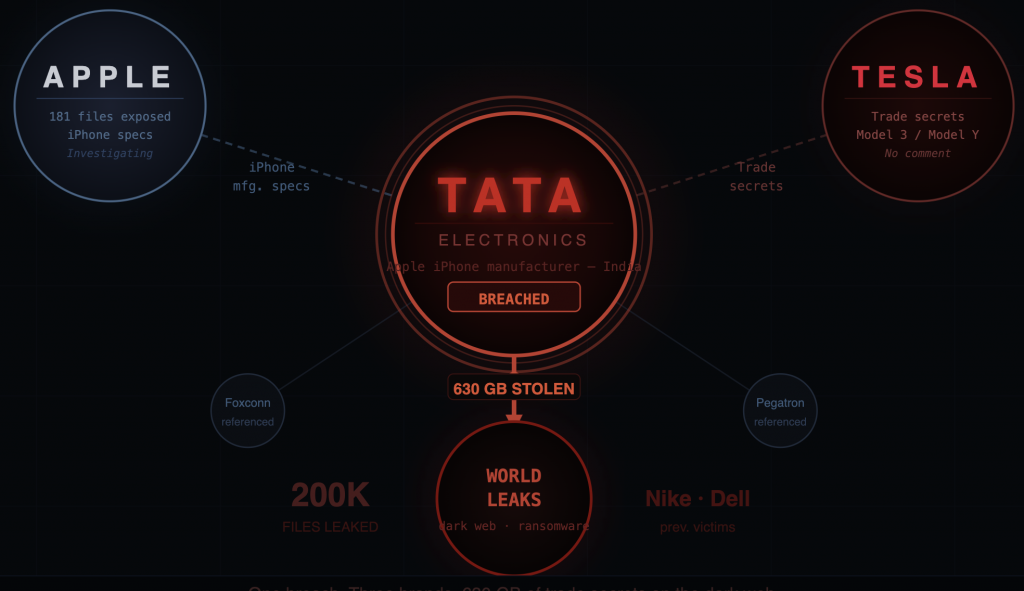
Supply chain network diagram showing Tata Electronics as the breached center node connected to Apple and Tesla, with World Leaks ransomware group stealing 630GB of trade secrets including iPhone manufacturing specs and Tesla engineering documents in June 2026.

630 GB. 200,000 Files. Apple and Tesla Trade Secrets. What the Tata Electronics Breach Means for Every Indian Manufacturer.

Somewhere in a factory in Tamil Nadu, assemblers are building iPhones. The process is precise, regulated, documented to an extraordinary degree. Quality inspection standards for circuit board components. Material specifications. Assembly procedures. Standard operating procedures for every machine on the floor. This documentation exists because Apple requires it. Because building one-third of the world’s most …

630 GB. 200,000 Files. Apple and Tesla Trade Secrets. What the Tata Electronics Breach Means for Every Indian Manufacturer. Read More »

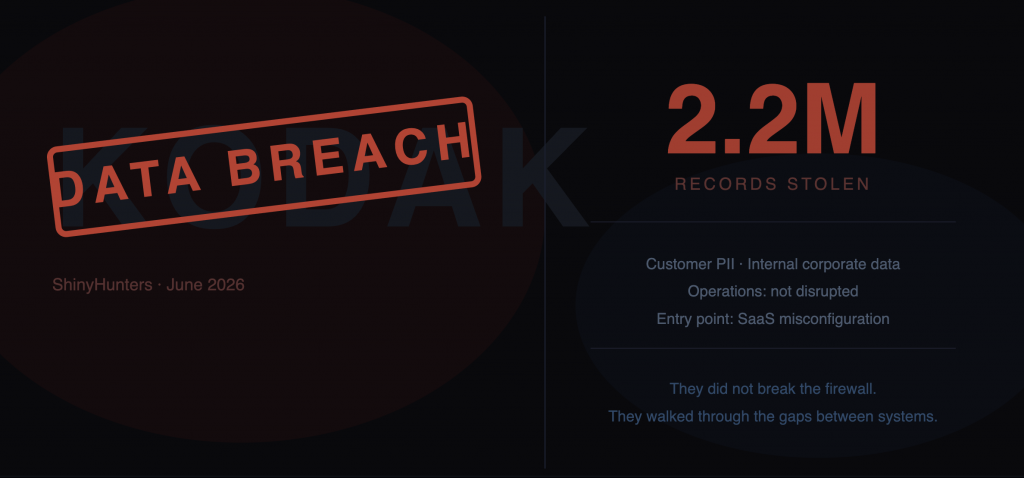
ShinyHunters claimed 2.2 million Kodak records in June 2026 through a SaaS misconfiguration, not a firewall breach. Blog cover for the Skeletos IT Services breakdown of the Kodak data breach and what Indian CTOs must do now.

2.2 Million Records. No Forced Entry. What the Kodak Breach Tells Every CTO About Their SaaS Stack.

On June 16, 2026, a message appeared on a dark web extortion portal. The target was Eastman Kodak Company. 130 years old. 79,000 patents. One billion dollars in annual revenue. A company that most people still associate with the yellow film boxes their parents used to buy, but which today operates as a serious business-to-business …

2.2 Million Records. No Forced Entry. What the Kodak Breach Tells Every CTO About Their SaaS Stack. Read More »

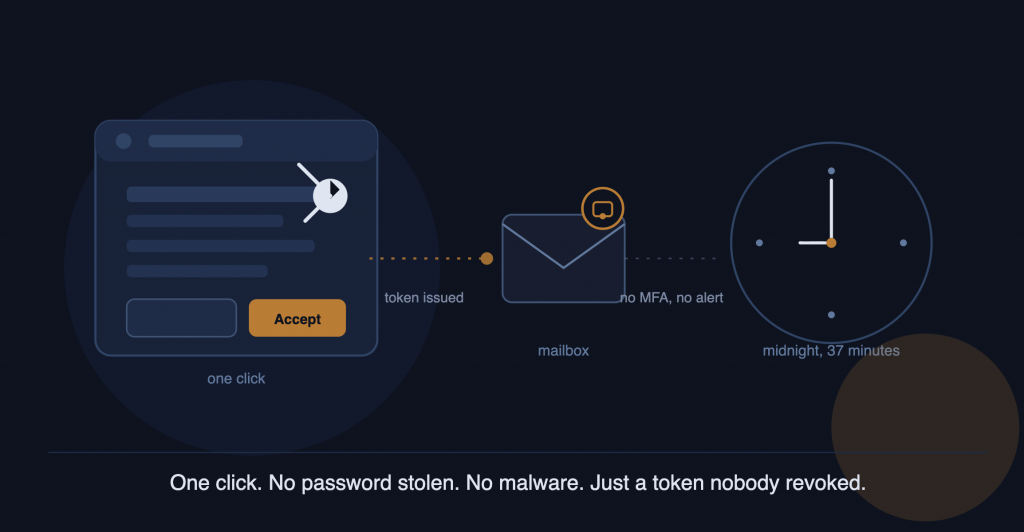
A single OAuth consent click let an attacker read and send email

It Took 03 Days to Find Out What That Click Had Done With OAuth

It started with an email that looked like nothing at all. A member of the sales and marketing team at a midsize insurance backend services company in India clicked a link. The link led to what looked like a normal Microsoft sign-in page. A box appeared asking for permission to connect a productivity app to …

It Took 03 Days to Find Out What That Click Had Done With OAuth Read More »

That Sentence Is a DPDP Problem | Skeletos.

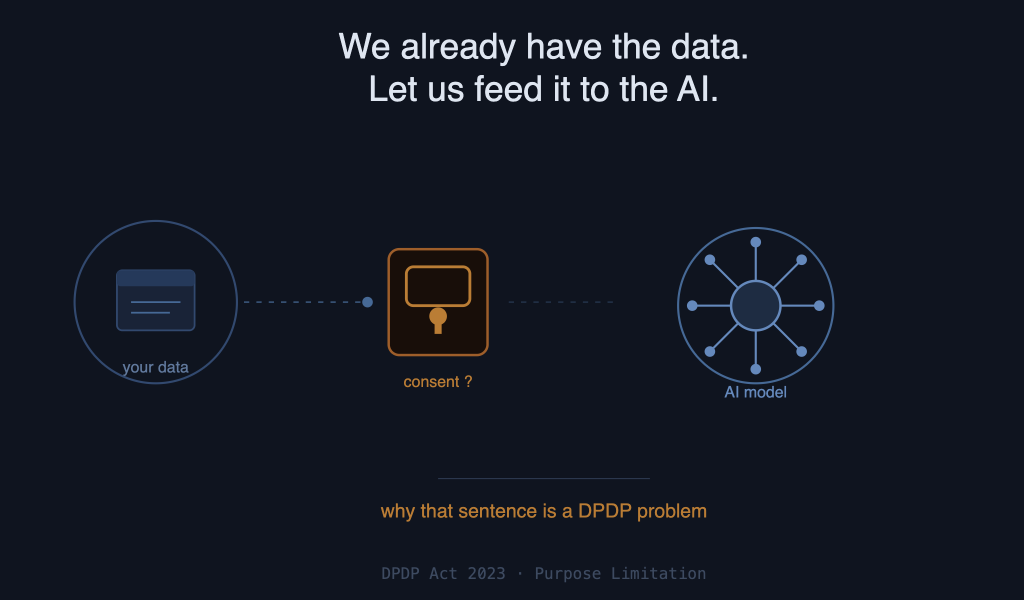
“We Already Have the Data. Let Us Feed It to the AI.” Why That Sentence Is a DPDP Problem

Rajan was genuinely excited. He is the CTO at a mid-size Gold Loan Company in Pune. Sharp, well-read, someone who follows global technology trends closely. We were sitting in his office last quarter when he pulled up a presentation from a vendor he had been speaking with for three weeks. The pitch was for an …

“We Already Have the Data. Let Us Feed It to the AI.” Why That Sentence Is a DPDP Problem Read More »

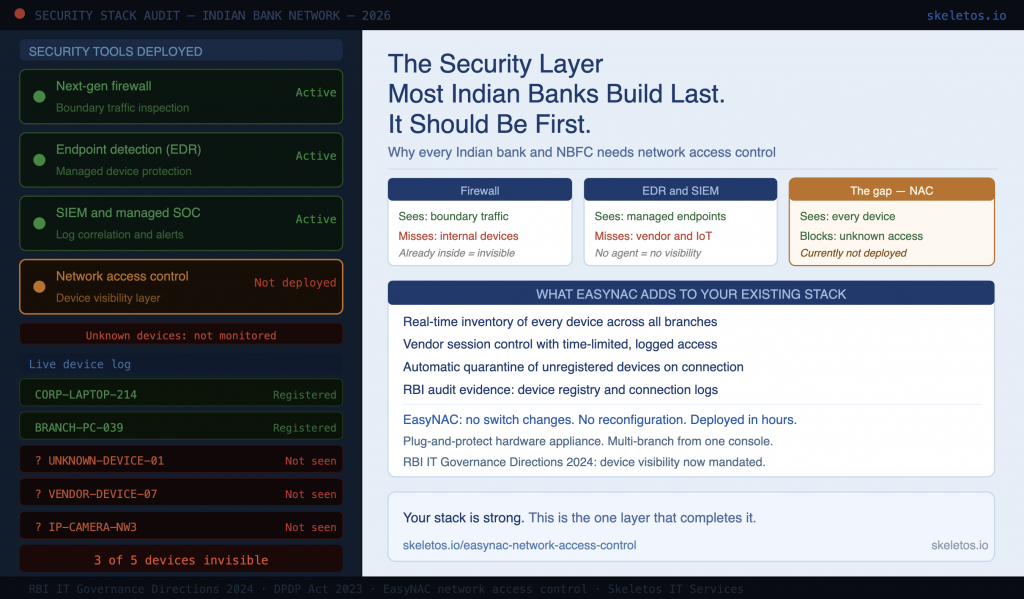
The Security Layer Most NBFC Build Last | Skeletos

The Security Layer Most NBFC’s Build Last. It Should Be First.

A few months ago, I was sitting in a security review meeting with the IT head of a mid-size NBFC in Pune. They had invested thoughtfully in their security stack. A next-generation firewall from a reputable vendor. Endpoint detection and response is deployed across every managed laptop and desktop. A SIEM feeds alerts to a …

The Security Layer Most NBFC’s Build Last. It Should Be First. Read More »

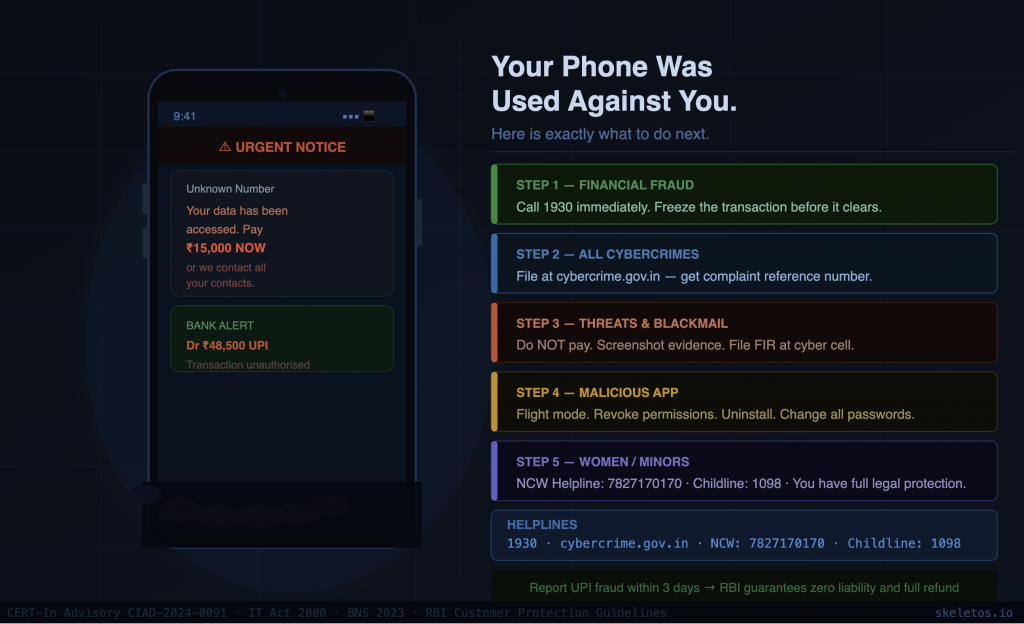
Your Phone Was Used Against You. Here Is Exactly What to Do Next.

Your Phone Was Used Against You. Here Is Exactly What to Do Next.

It started with a Phone message that looked completely ordinary. A link that promised a job application form. A notification from what appeared to be a courier company asking you to update a delivery address. A QR code shared in a WhatsApp group by someone you thought you knew. You tapped it. Within minutes, an …

Your Phone Was Used Against You. Here Is Exactly What to Do Next. Read More »

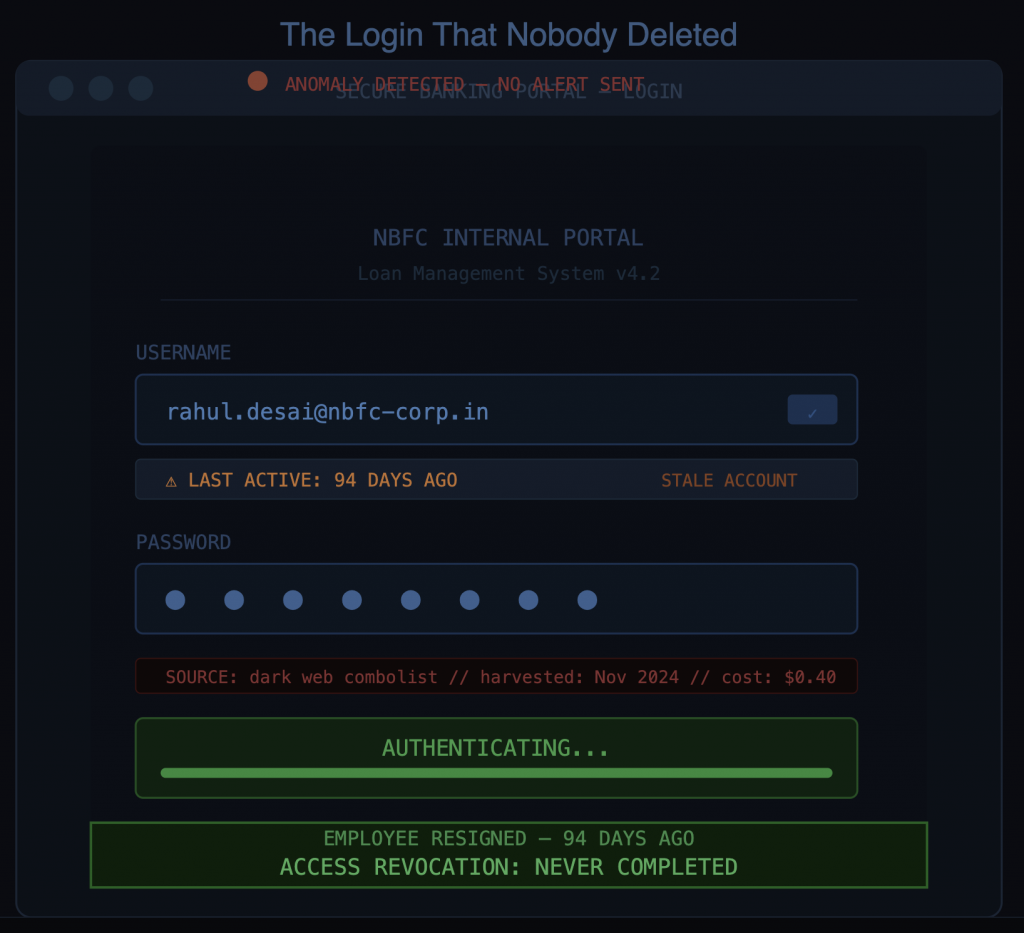
The Employee Login Credentials That Nobody Deleted

The Login That Nobody Deleted. How Stale Credentials Are Becoming India’s Fastest-Growing Cyber Threat.

On the morning of March 29, 2025, members of five major Australian superannuation funds woke up to find their retirement accounts had been accessed overnight. Not by a single attacker hitting a single fund with a sophisticated exploit. By a coordinated campaign that hit AustralianSuper, Rest Super, Hostplus, Australian Retirement Trust, and Insignia Financial simultaneously. …

The Login That Nobody Deleted. How Stale Credentials Are Becoming India’s Fastest-Growing Cyber Threat. Read More »

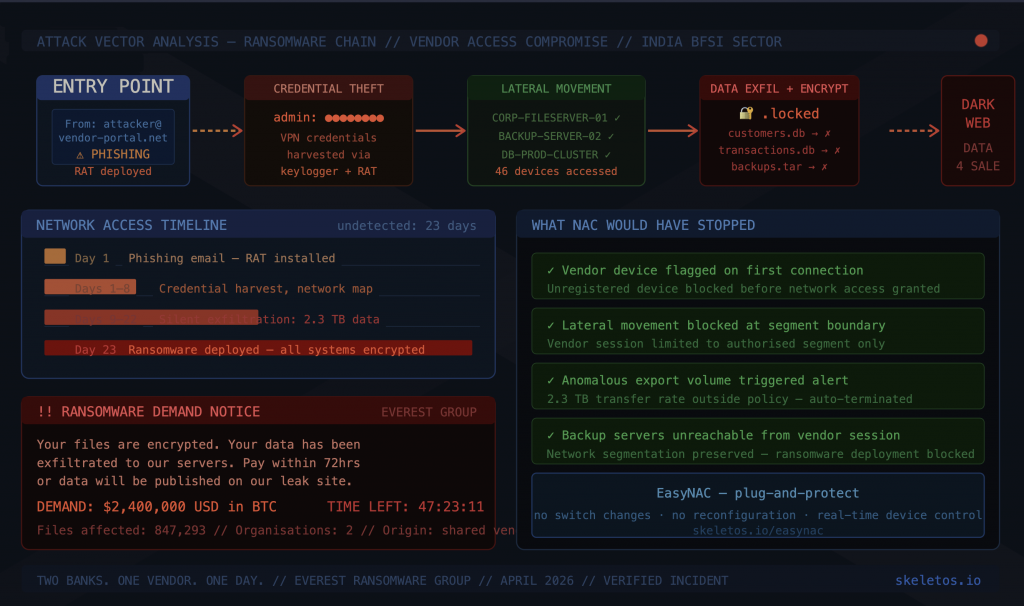
Two Banks. One Vendor. One Day. | Skeletos

2 Banks 1 Vendor. The Third-Party Risk Pattern Indian NBFCs Cannot Ignore.

On April 20, 2026, the Everest Ransomware Group posted the names of two banks on its dark web leak site. Both were major banks. Both appeared on the same day. Both had their customer and document data offered for sale to the highest bidder in criminal markets. The two banks had not been breached separately …

2 Banks 1 Vendor. The Third-Party Risk Pattern Indian NBFCs Cannot Ignore. Read More »