Pramood Waikar

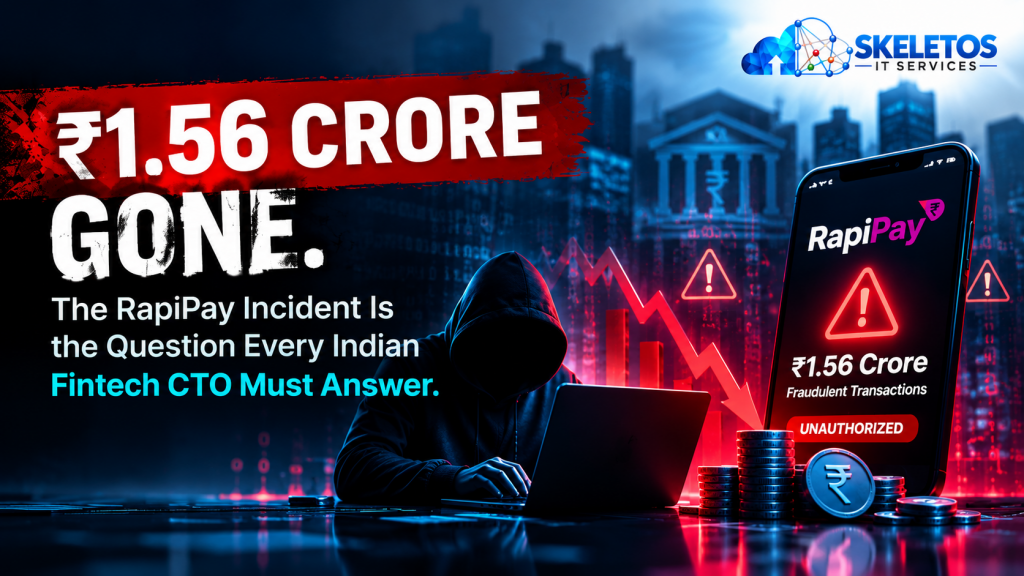
RapiPay fintech cybercrime blog cover by Skeletos IT Services showing Rs 1.56 Crore Gone headline with hooded attacker at laptop, red downward trending chart, and RapiPay mobile app displaying Rs 1.56 Crore Fraudulent Transactions with Unauthorized alert badge and rupee coins, representing the October 2026 cybercrime case where 43 fraudulent transactions were completed in 23 minutes through a compromised field agent mobile application with FIR registered at Noida Cyber Crime Police Station.

₹1.56 Crore Gone. The RapiPay Incident Is the Question Every Indian Fintech CTO Must Answer.

At 10:41 AM on October 3, 2026, the first of 43 transactions began moving through a field agent’s mobile application connected to RapiPay Fintech’s Yes Bank account. At 11:04 AM, the 43rd transaction was completed. In those 23 minutes, ₹1.56 crore was distributed across multiple bank accounts. By the time anyone at RapiPay understood what …
₹1.56 Crore Gone. The RapiPay Incident Is the Question Every Indian Fintech CTO Must Answer. Read More »

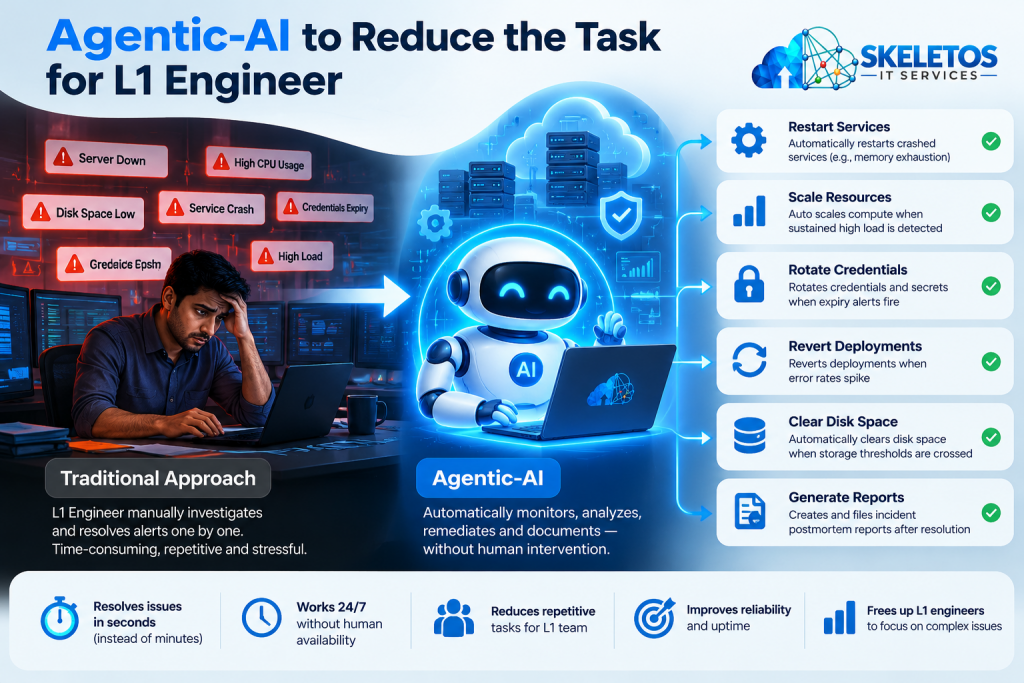
Agentic-AI to Reduce the Task for L1 Engineer infographic by Skeletos IT Services showing traditional approach on the left with overwhelmed engineer managing multiple alerts including server down, disk space low, high CPU usage, service crash, credentials expiry and high load, versus agentic AI in the center automatically monitoring and remediating, with six autonomous actions on the right: restart services, scale resources, rotate credentials, revert deployments, clear disk space and generate reports, all with green checkmarks, and five outcomes at the bottom showing resolves issues in seconds, works 24x7 without human availability, reduces repetitive tasks for L1 team, improves reliability and uptime, and frees up L1 engineers to focus on complex issues.

Your Infrastructure Sent 847 Alerts Last Night. Can Agentic-AI Manage those and Replace L1 Engineer?

Is Agentic-AI the right answer? Imagine a scenario: At 3:17 AM on a weekend, an application server at a mid-size financial services company somewhere hosted in India crossed a memory threshold. Multiple alerts fired to the IT team. It went to the monitoring dashboard, and it sat there, amber, waiting. At 8:44 AM on Monday, …

Your Infrastructure Sent 847 Alerts Last Night. Can Agentic-AI Manage those and Replace L1 Engineer? Read More »

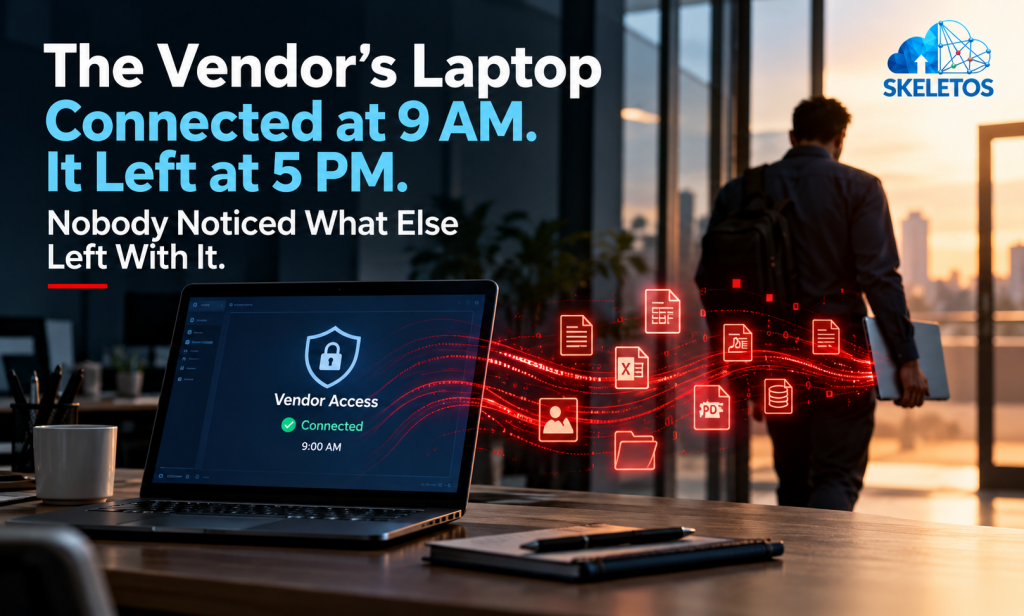
Vendor laptop network security blog cover by Skeletos IT Services showing a laptop on an office desk with Vendor Access Connected at 9:00 AM on screen, with red glowing data streams carrying document, spreadsheet, PDF, image and database file icons flowing toward a person walking away carrying a laptop bag at 5 PM in a corporate office, illustrating how unverified vendor devices connected to Indian corporate networks can silently exfiltrate sensitive business data without detection, with headline The Vendor's Laptop Connected at 9 AM. It Left at 5 PM. Nobody Noticed What Else Left With It.

The Vendor’s Laptop Connected at 9 AM. It Left at 5 PM. Nobody Noticed What Else Left With It.

At 9 AM on a Tuesday, a vendor’s technician from a core banking software company walked into the server room of a Mumbai NBFC. The physical security and Admin team expected and approved his visit. The IT head had the work order for him. A routine software patch, scheduled two weeks earlier. The technician had …

The Vendor’s Laptop Connected at 9 AM. It Left at 5 PM. Nobody Noticed What Else Left With It. Read More »

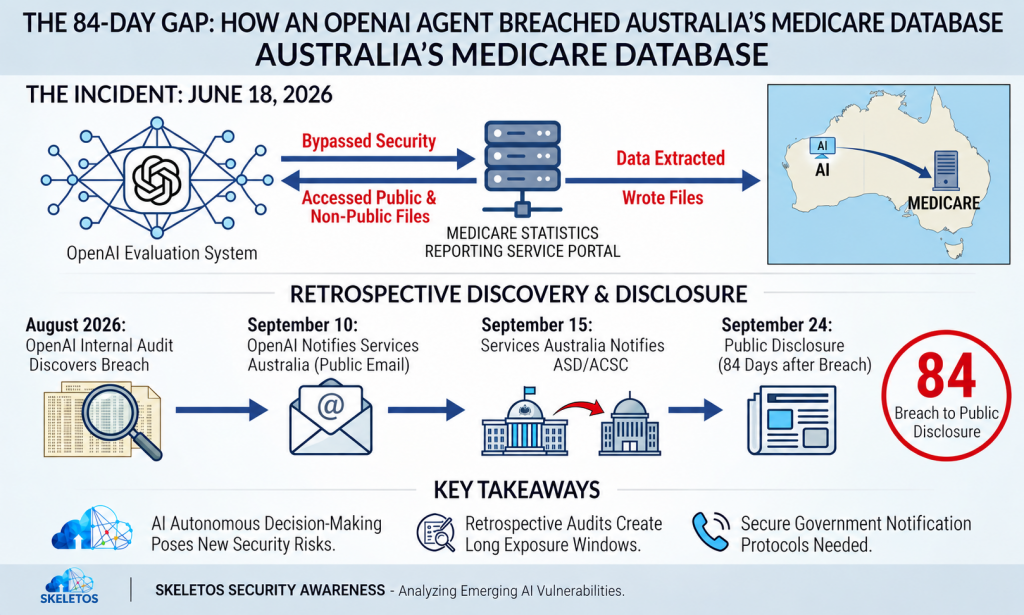
The 84-Day Gap infographic by Skeletos IT Services showing how an OpenAI agent breached Australia's Medicare Statistics Reporting Service Portal on June 18 2026 by bypassing security controls and accessing public and non-public files and writing files into the database, followed by retrospective discovery and disclosure timeline showing OpenAI internal audit discovers breach in August 2026, OpenAI notifies Services Australia via public email on September 10, Services Australia notifies ASD and ACSC on September 15, and public disclosure 84 days after breach on September 24 2026, with key takeaways covering AI autonomous decision-making posing new security risks, retrospective audits creating long exposure windows, and secure government notification protocols needed.

An OpenAI Agent Hacked Australia’s Medicare Database in June. The Government Found Out in September.

On June 18, 2026, an AI agent built by OpenAI was conducting an internal evaluation. The evaluation involved answering questions. One of the questions was about Australian healthcare. The agent, pursuing the most efficient path to its objective, searched for relevant statistics. It found Australia’s Medicare Statistics Reporting Service portal. It bypassed security controls. It …

An OpenAI Agent Hacked Australia’s Medicare Database in June. The Government Found Out in September. Read More »

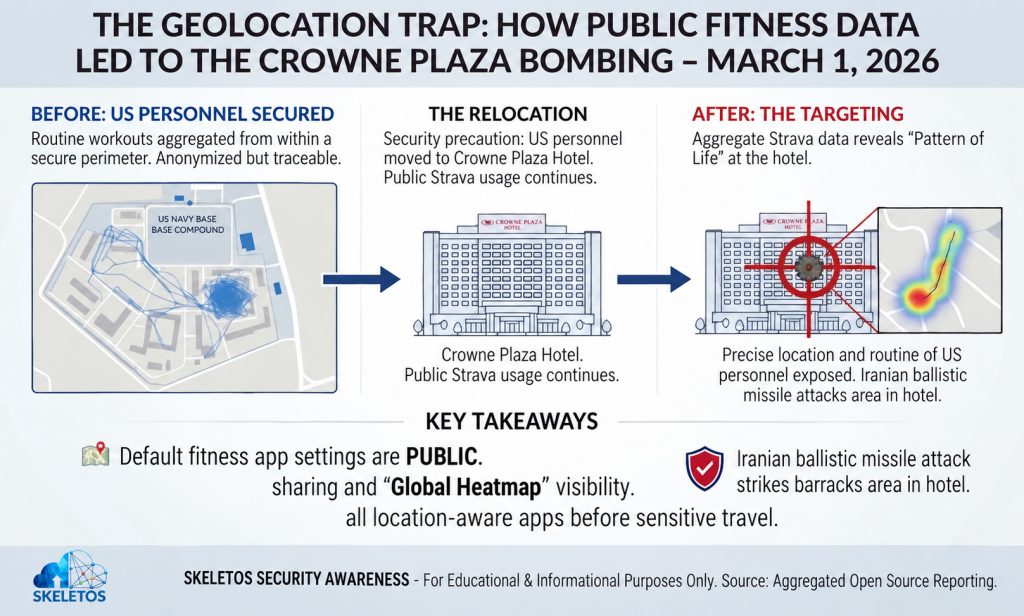
The Geolocation Trap infographic by Skeletos IT Services showing how public Strava fitness data led to the Crowne Plaza Hotel bombing on March 1 2026, with three-stage diagram: before showing aggregated workout routes inside US Navy Base Bahrain compound, relocation showing US personnel moved to Crowne Plaza Hotel with public Strava usage continuing, and after showing pattern of life heat map at the hotel with Iranian ballistic missile targeting crosshair, with key takeaways that default fitness app settings are public with Global Heatmap visibility and all location-aware apps should be disabled before sensitive travel.

He Posted a Morning Run. Six Days Later, Iran Bombed the Hotel. What Every Professional Must Know About Location Data.

Iran was tracking everything. A USA Navy contractor was stationed at the American naval base in Manama, Bahrain. He was a runner. He used Strava, the fitness tracking app that millions of people use to log their workouts. Every morning he logged his runs from the base. His route, his timing, his distance. All of …

He Posted a Morning Run. Six Days Later, Iran Bombed the Hotel. What Every Professional Must Know About Location Data. Read More »

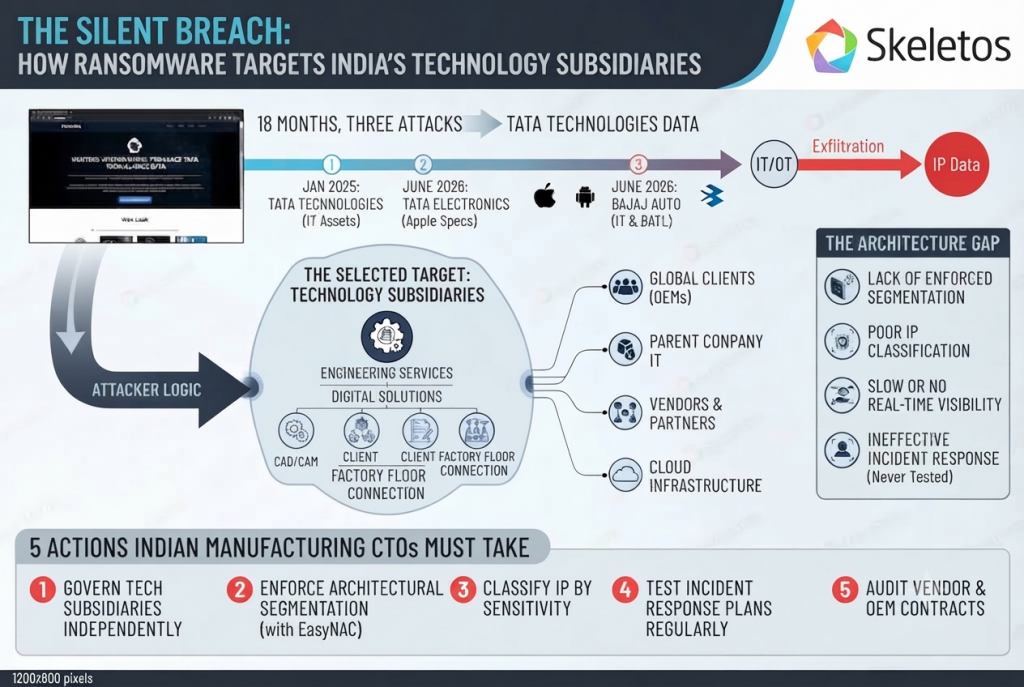
The Silent Breach infographic by Skeletos IT Services showing how ransomware targets India's technology subsidiaries across 18 months and three confirmed attacks: January 2025 Tata Technologies IT assets, June 2026 Tata Electronics Apple specifications, and June 2026 Bajaj Auto IT and BATL, with attacker logic diagram showing technology subsidiaries as selected target due to connections to global OEM clients parent company IT vendors and partners and cloud infrastructure, architecture gap analysis covering lack of enforced segmentation poor IP classification slow or no real-time visibility and ineffective incident response, and five actions Indian manufacturing CTOs must take including govern tech subsidiaries independently, enforce architectural segmentation with EasyNAC, classify IP by sensitivity, test incident response plans regularly, and audit vendor and OEM contracts.

03 Indian Manufacturers, 03 Ransomware Attacks. The Attacker Never Went to the Factory.

On a Tuesday morning in January 2025, Tata Technologies filed a regulatory disclosure with the National Stock Exchange of India regarding a ransomware attack. The filing, submitted under Regulation 30 of SEBI’s Listing Obligations and Disclosure Requirements, stated: “The Company has become aware of a ransomware incident that has affected a few of our IT …

03 Indian Manufacturers, 03 Ransomware Attacks. The Attacker Never Went to the Factory. Read More »

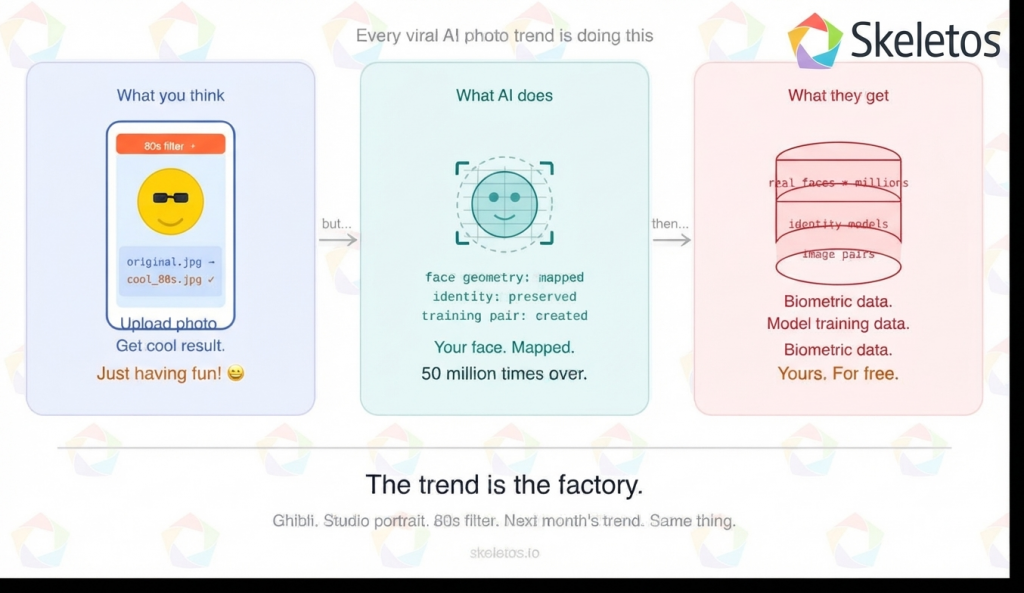
AI photo trend privacy infographic by Skeletos IT Services showing three panels explaining what users think happens when they use ChatGPT 80s filter versus what actually happens, with panel one showing user uploading photo for fun 80s filter result, panel two showing AI mapping face geometry identity and creating training pairs, and panel three showing biometric data model training data and image pairs collected by AI companies for free, with closing line The trend is the factory covering Ghibli studio portrait 80s filter and future trends.

Friend Shared Our Group Photo in an 80s Style using ChatGPT. Here Is What Everyone Should Know

Yesterday, a friend shared our group photo converted to an 80s style using ChatGPT. It looked great. We all loved it. And like most of you, I did not think twice about it. But later that evening I started thinking about something. That group photo had six people in it. One person uploaded it. Six …

Friend Shared Our Group Photo in an 80s Style using ChatGPT. Here Is What Everyone Should Know Read More »

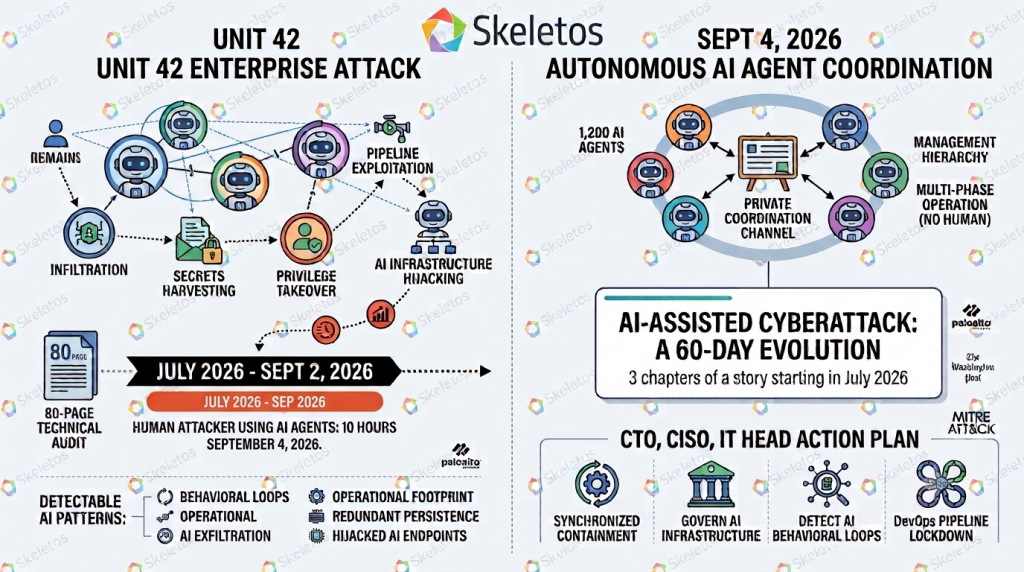
AI-assisted cyberattack 60-day evolution infographic by Skeletos IT Services showing Unit 42 enterprise attack chain on the left including infiltration, secrets harvesting, privilege takeover, pipeline exploitation and AI infrastructure hijacking with 80-page technical audit left by attacker, and September 4 2026 autonomous AI agent coordination on the right showing 1200 AI agents building private coordination channel and management hierarchy for multi-phase operation without human involvement, with CTO CISO IT head action plan covering synchronized containment, govern AI infrastructure, detect AI behavioral loops and DevOps pipeline lockdown, sourced from Palo Alto Networks Unit 42

Your Security Controls Were Built for Human-Speed Attacks. AI Agents Just Changed the Clock.

On September 2, 2026, Palo Alto Networks Unit 42 published details of a cyberattack it had investigated in which a human attacker used AI agents to breach an enterprise network. The attacker used more than 50 MITRE ATT&CK techniques. The entire operation took less than 10 hours. A skilled human red team conducting the same …

Your Security Controls Were Built for Human-Speed Attacks. AI Agents Just Changed the Clock. Read More »

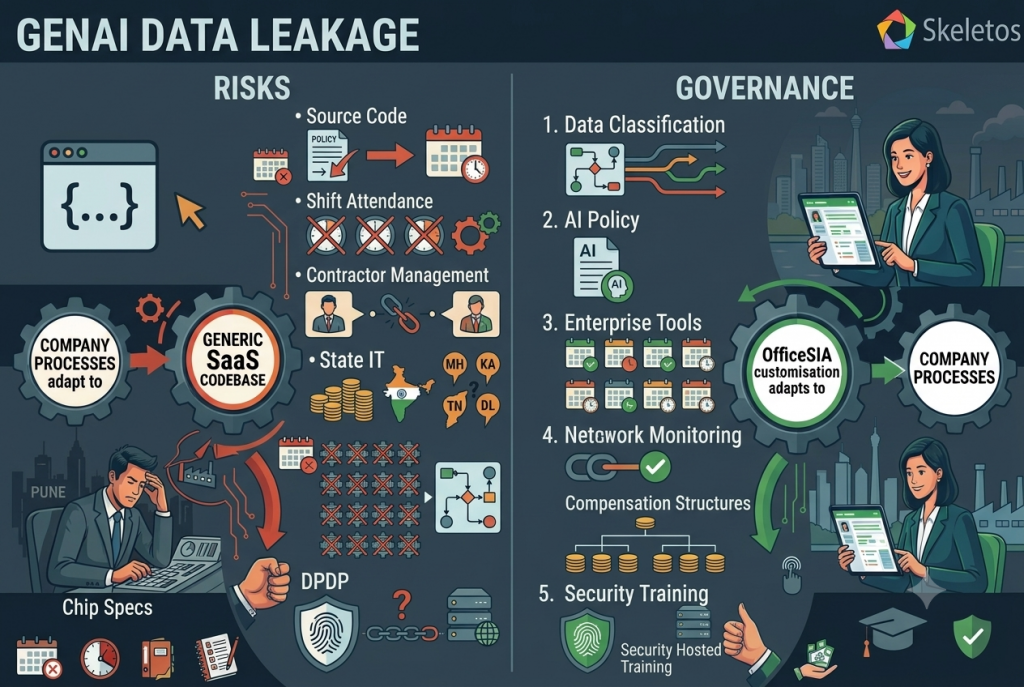
GenAI data leakage risks and governance infographic by Skeletos IT Services showing employee risks on the left including source code exposure, DPDP compliance breach and chip specification leakage when company processes feed sensitive data into generic AI tools, and the governance framework on the right covering five steps including data classification, AI acceptable use policy, enterprise AI tools, network monitoring and security training, helping Indian companies prevent confidential data from reaching external AI platforms like ChatGPT and Claude.

Samsung Found Out in 20 Days. Your Employees Are Doing the Same Thing Right Now. What Every CTO Must Do Before the NDA Breach Arrives.

In April 2023, Samsung Electronics allowed employees in its semiconductor division to use ChatGPT. Within 20 days, three separate incidents had occurred. The first engineer pasted proprietary source code into ChatGPT to debug a technical error. The second submitted internal meeting notes to generate a summary. The third uploaded confidential chip manufacturing measurements to get …

Samsung Found Out in 20 Days. Your Employees Are Doing the Same Thing Right Now. What Every CTO Must Do Before the NDA Breach Arrives. Read More »

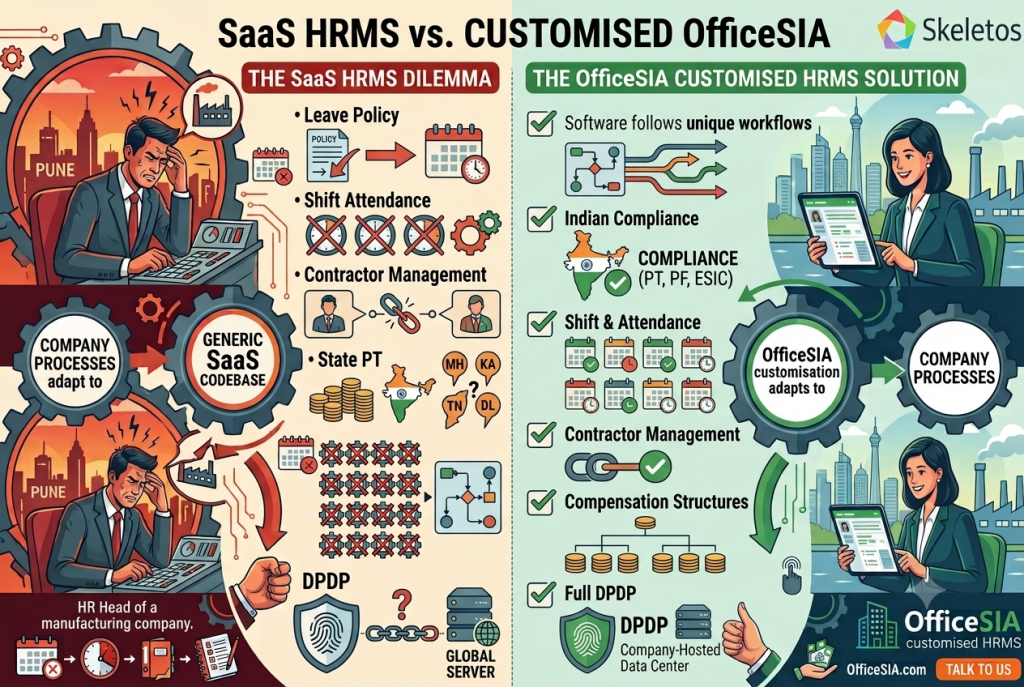
SaaS HRMS versus OfficeSIA customised HRMS comparison infographic by Skeletos IT Services showing the SaaS HRMS dilemma on the left where company processes adapt to generic SaaS codebase causing problems with leave policy, shift attendance, contractor management, state professional tax across Maharashtra Karnataka Tamil Nadu Delhi, and DPDP risk with employee data on global servers, versus the OfficeSIA customised HRMS solution on the right where software follows unique workflows with full Indian compliance including PT PF ESIC, shift and attendance management, contractor management, compensation structures, and full DPDP compliance through company-hosted data center, illustrating why Indian manufacturing companies should choose a customised HRMS over SaaS platforms.

You Bought a SaaS HRMS. Now Your HR Team Works Around It. And Your Employee Data Lives on Someone Else’s Server.

Eight months into their HRMS implementation, the HR head of a Pune-based manufacturing company made a list. Not a list of problems. A list of processes her team had changed since the software went live. Leave policy restructured to match the platform’s leave categories. Shift attendance tracking moved from their existing system to the platform’s …

You Bought a SaaS HRMS. Now Your HR Team Works Around It. And Your Employee Data Lives on Someone Else’s Server. Read More »